Enkrypt AI Recognized as a Gartner® Cool Vendor in AI Security 2025


A milestone that reflects our leadership in securing agentic, multimodal AI for the enterprise.
This recognition highlights the growing importance of safeguarding innovation and reinforces our role as a trusted partner for enterprises navigating today’s most pressing agentic AI risks.
Agentic, multimodal AI raises the stakes because systems don’t just answer—they act across text, images, and voice. The risks are operational, not theoretical: a poisoned screenshot or PDF can redirect an agent’s tools; a spoofed voice can trigger approvals; a single bad instruction can cascade into wire transfers, account changes, or unlogged policy decisions that won’t survive audit. When agents can see, decide, and do, risk scales with capability. That’s exactly the gap we’ve been building to close.
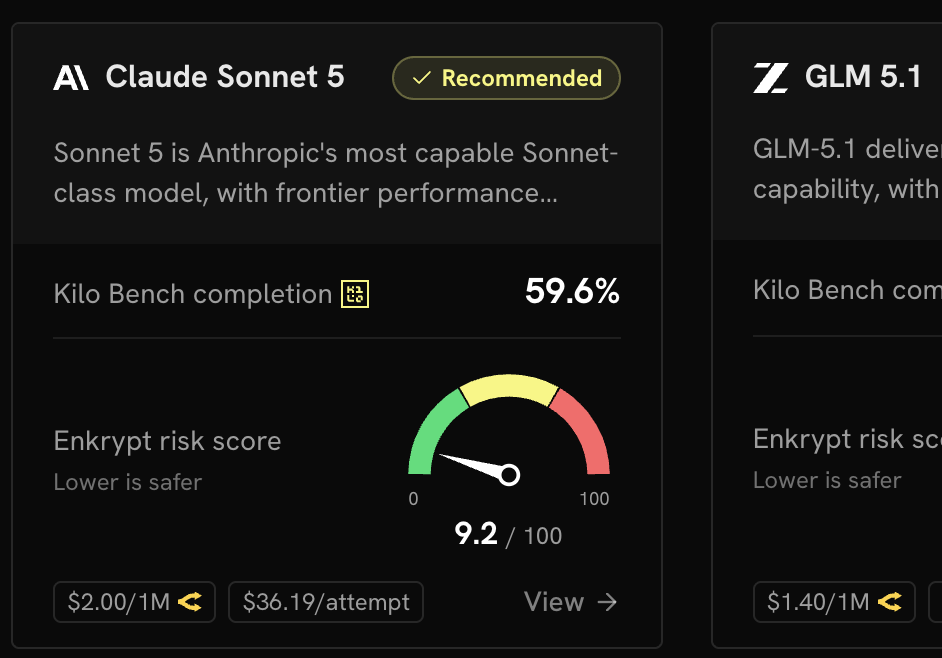
We provide real-time guardrails across text, images, and voice, stopping harmful or non-compliant actions before they cause damage. Enkrypt AI has also introduced the industry's first LLM and Agent Safety Leaderboard, giving organizations a clear way to evaluate models not only by performance but also by their risk profile.
What makes this recognition meaningful is not just the technology we have built, but the trust our customers have placed in us. From Fortune 500 leaders in finance and healthcare to innovators in retail, manufacturing, and logistics, we witness daily how essential security and compliance are to unlocking the next wave of progress.
This milestone is a reminder of the responsibility we carry to help organizations move forward with confidence, balancing innovation with the trust and accountability their stakeholders expect.
Sahil Agarwal, CEO and Co-Founder, Enkrypt AI
Disclaimer:
Gartner, Cool Vendors in AI Security, Jeremy D'Hoinne, Bart Willemsen, Dennis Xu, Avivah Litan, 24 September 2025.
Gartner is a registered trademark and service mark and Cool Vendors is a registered trademark of Gartner, Inc. and/or its affiliates in the U.S. and internationally and are used herein with permission. All rights reserved.
Gartner does not endorse any vendor, product or service depicted in its research publications and does not advise technology users to select only those vendors with the highest ratings or other designation. Gartner research publications consist of the opinions of Gartner’s research organization and should not be construed as statements of fact. Gartner disclaims all warranties, expressed or implied, with respect to this research, including any warranties of merchantability or fitness for a particular purpose.
Frequently Asked Questions
Agent guardrails are real-time security controls that stop harmful or non-compliant actions before agents execute them across text, images, and voice. They prevent operational risks like tool misuse, data leakage, and unauthorized decisions.
- Block poisoned screenshots or PDFs from redirecting agent tools
- Stop spoofed voice commands from triggering approvals or transfers
- Enkrypt AI delivers ultra-low latency runtime protection for multimodal systems
Securing agentic AI requires real-time guardrails across all modalities, red-teaming across risk categories, and centralized policy enforcement. Enkrypt AI covers 300+ red-teaming risk categories to identify vulnerabilities before deployment.
- Test agents against prompt injection, data exfiltration, and tool misuse scenarios
- Enforce policies consistently across text, image, and voice inputs
- Monitor and block harmful actions at runtime with millisecond response times
Red teaming identifies vulnerabilities in agents before production; guardrails block attacks in real time during operation. Both are essential—red teaming finds gaps, guardrails prevent exploitation.
- Red teaming simulates 300+ attack scenarios across risk categories
- Guardrails enforce policies and stop harmful actions instantly
- Together they reduce manual compliance effort by up to 90%
Enkrypt AI is recognized as a Gartner Cool Vendor in AI Security 2025 for securing agentic and multimodal AI at enterprise scale. The platform delivers real-time guardrails, red-teaming, and policy-based governance across all modalities.
- Protects agents that process text, images, voice, and tool calls
- Benchmarks 200+ LLMs on the public safety leaderboard for risk evaluation
- Trusted by Fortune 500 leaders in finance, healthcare, retail, and logistics
Since agentic AI risks scale with capability, seeing how Enkrypt AI's real-time guardrails work on your agents matters. Book a demo to evaluate your risk profile, or start a free trial to test it yourself.